What the landmark PINlogger research proved, what modern iPhone, Android and browser protections have changed, and when suspected surveillance requires forensic investigation.
By Navid Sobbi, Founder and CEO, NSI Global
ORIGINAL PUBLICATION: 8 March 2020 REVISION COMPLETED: 21 September 2026 AEST
Yes – smartphone sensors can reveal more about a user than many people realise. Motion, orientation, location, microphone, camera, Bluetooth and other data sources can expose patterns about how a device is being used and, under some conditions, can support side-channel attacks that infer sensitive information. But the risk in 2026 is more nuanced than the original headlines about sensors “stealing” PINs suggested.
The landmark Newcastle University research that inspired the original version of this article was a genuine proof of concept. It showed that motion and orientation data could be analysed to infer four-digit PIN entry under defined experimental conditions. Since then, mobile operating systems and browsers have added substantial permission, rate-limiting and privacy controls. Those protections reduce some attack paths, but they do not make every sensor harmless or eliminate the wider problem of mobile surveillance.
The most important distinction is this: sensor leakage is not the same thing as spyware. Spyware is not the same thing as account compromise. Account compromise is not the same thing as telecommunications-network interception. And none of those automatically rules out a physical listening device in the room. A credible investigation starts by identifying which technical layer could explain the concern.
The Short Answer: Can Phone Sensors Spy on You?
Sensor data can contribute to privacy loss or side-channel inference, but the answer depends on the sensor, operating system, browser or application, permissions, sampling rate, background behaviour and the attacker’s access. A single statement such as “apps can read all sensors without permission” is no longer technically accurate across modern iPhone, Android and web environments.
| Threat Layer | Requires Conventional Malware? | What It Uses | Typical Evidence Source | NSI-Relevant Response |
| Sensor side channel | Not necessarily | Motion, orientation or other sensor data used to infer behaviour | App/browser behaviour, permissions, logs, device artefacts and research context | Mobile forensic and security assessment |
| Malicious or over-permissioned app | An installed app is involved | Permissions, background access, local data and network connections | Installed apps, permission state, logs, network artefacts and application data | Digital forensics and compromise assessment |
| Mercenary spyware / advanced malware | Yes, in the broad sense of device compromise | Exploit chains, privileged access and covert collection | Forensic artefacts, device logs, application/system evidence and indicators of compromise | Specialist spyware and malware forensics |
| Account or cloud compromise | No device malware required | Credentials, sessions, linked devices, cloud services | Account logs, cloud records, session history and authorised account data | Account/cloud forensics and incident response |
| Telecommunications-network surveillance | No conventional handset spyware required | Network signalling or telecommunications infrastructure | Network-side evidence, signalling analysis and communications-security assessment | COMSEC / telecommunications security assessment |
| Physical eavesdropping | No | Hidden microphones, cameras, trackers or external collection systems | Physical environment, RF/electronic indicators and device evidence | TSCM bug sweep and technical inspection |
What Counts as a Smartphone Sensor?
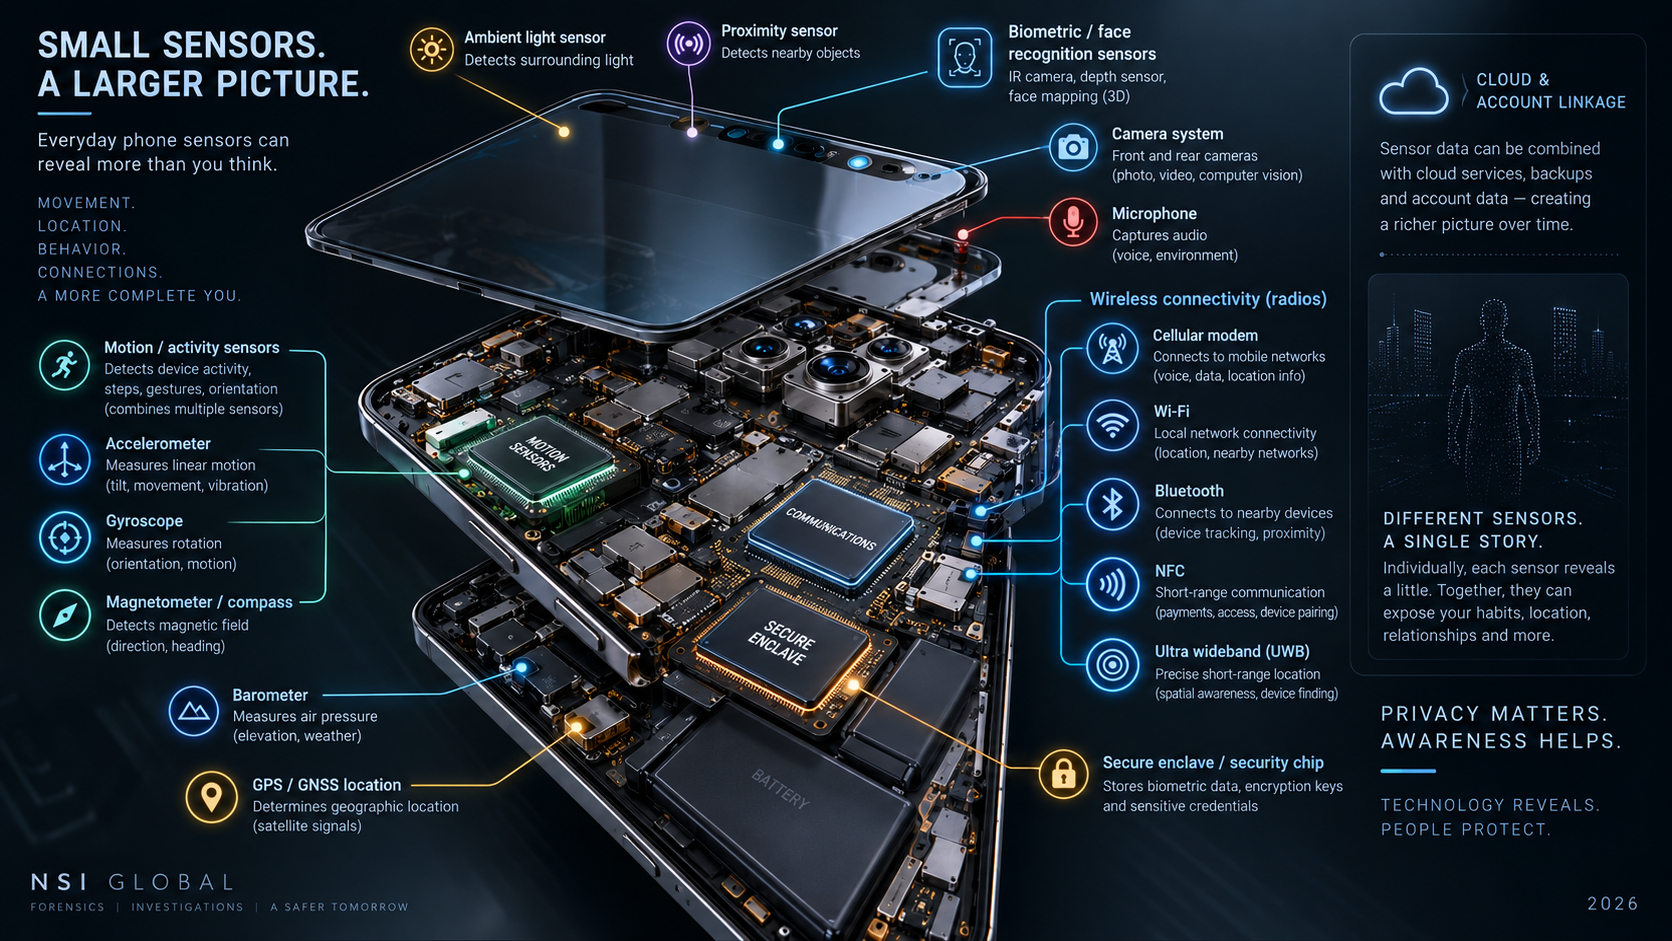
Modern phones combine physical sensors, radios, cameras, microphones and software-derived signals. Some measure movement or orientation; others describe location, proximity, environmental conditions or biological activity. The privacy rules are not identical for every category.
- Motion and orientation sensors – accelerometer, gyroscope and related orientation data can describe how the device moves, tilts and rotates.
- Location systems – GNSS/GPS, Wi-Fi and other location inputs can reveal where a device is or has been, subject to platform controls and service configuration.
- Camera and microphone – high-value sensors that modern platforms place behind explicit privacy controls and visible use indicators.
- Bluetooth and local-network access – can reveal or interact with nearby devices and environments and are increasingly governed by dedicated permissions.
- Magnetometer, proximity, ambient-light and other environmental sensors – useful for legitimate device functions but potentially informative in specialised side-channel research.
- Health and body sensors – heart rate and related health data are increasingly protected by granular permission models, particularly on current Android/Wear OS and Apple platforms.
A sensor does not need to record a conversation or take a photograph to create privacy risk. Side-channel analysis is about extracting information indirectly from patterns that were generated for another purpose.
The Research That Put Mobile Sensor Side Channels on the Map
In 2017, researchers at Newcastle University published “Stealing PINs via Mobile Sensors: Actual Risk versus User Perception”. Their proof-of-concept, PINlogger.js, used JavaScript to collect motion and orientation sensor streams from an Android phone and applied a neural-network classifier to infer PIN entry.
On the paper’s test set of fifty four-digit PINs, the researchers reported 74% correct identification on the first attempt, increasing to 86% on the second attempt and 94% on the third. The key finding was not that every website could automatically discover every user’s PIN. It was that motion and orientation data, which users generally considered less sensitive than camera or GPS access, could carry enough behavioural information to support a meaningful side-channel attack under experimental conditions.
The original 2020 NSI article drew on that research, but it repeated the 2017 platform assumption that websites and applications could access most sensors without permission. That statement now requires qualification. The security model has changed materially since the research was conducted.
What Has Changed Since the 2017 PINlogger Research?
Modern platforms have introduced several layers of protection that did not exist, or were not as mature, when the original research was conducted. The details differ between Apple, Android and the web platform, so it is important not to compress them into a single rule.
| Platform / Layer | Current Protection Example | What It Means | Important Limitation |
| iPhone / iPad apps | Apple exposes privacy controls for camera, microphone, Bluetooth, Motion & Fitness, Local Network and other categories. | Users can review and revoke access for many sensitive data and hardware functions. | Permission controls do not prove that a device is uncompromised or explain every form of side-channel behaviour. |
| Apple App Privacy Report | Shows recent access to privacy-sensitive data/sensors and app/network activity after the report is enabled. | Can help users identify unexpected access patterns or network contacts. | It is a transparency tool, not a forensic certificate that advanced spyware is absent. |
| Android motion sensors | Apps targeting Android 12 or later are subject to sampling-rate limits for certain motion and position sensors; higher-rate access requires HIGH_SAMPLING_RATE_SENSORS. | The platform reduces unrestricted high-frequency collection through ordinary sensor APIs. | Not every motion sensor is governed by the same user-facing runtime prompt, and behaviour varies by API and target version. |
| Android health/body sensors | Recent Android versions use increasingly granular permissions for health and body-sensor data. | Sensitive health telemetry has stronger permission separation and background-access controls. | This does not automatically apply to every general-purpose motion sensor. |
| Web sensor APIs | Modern web APIs can require HTTPS, sensor permissions and/or Permissions-Policy controls; motion/orientation permission APIs exist in supported browsers. | Websites have more constrained access than the broad 2017 assumption suggests. | Browser support and exact permission behaviour still vary, so no universal browser rule should be assumed. |
Can Apps and Websites Still Access Motion Sensors Without Permission?
Sometimes – but not as a universal rule. The answer depends on the platform, sensor and API. Camera, microphone, location, Bluetooth and many health-related data classes are subject to explicit platform permissions. Apple also exposes Motion & Fitness controls to users. On Android, certain motion sensors remain available through native sensor APIs without the same style of runtime prompt used for camera or microphone, but Android applies sampling-rate restrictions to modern apps and requires an additional permission for higher-rate sensor collection.
On the web, the picture is similarly mixed. The Generic Sensor APIs use secure-context and permission mechanisms, while device-motion and device-orientation events have evolved toward explicit permission request models in supported browsers. Permissions-Policy can also restrict whether a document is allowed to use accelerometer, gyroscope or magnetometer interfaces. Browser support remains uneven, which is precisely why modern advice should avoid absolute statements.
Can an Accelerometer or Gyroscope Really Reveal a PIN?
The 2017 Newcastle research demonstrated that it can be possible to infer PIN entry from motion/orientation data under controlled conditions. It did not establish that any random app or website can reliably recover a user’s passcode in normal real-world conditions.
Successful inference depends on the quality and frequency of sensor data, the way the user holds and interacts with the device, the model used to interpret the signal, the available training data, the device and browser or app environment, and modern platform restrictions. The correct conclusion is therefore that motion data can be security-sensitive – not that a gyroscope is equivalent to a keylogger.
What Can Sensor Data Potentially Reveal?
Depending on the sensor and context, data streams can reveal or help infer information such as device movement, orientation, physical activity, location, environmental context and patterns of interaction. Academic research has also explored side channels that use motion, acoustic, power, timing and other indirect signals to infer user activity.
The evidential strength of those inferences varies. A forensic examiner should distinguish between what a sensor directly recorded, what an application or account logged, and what is merely inferred from a statistical model. That distinction matters in corporate investigations, litigation and expert evidence.
Sensor Leakage Is Not the Same as Spyware
A sensor side channel normally exploits information that a device or application is legitimately able to observe, then derives a secondary inference from it. Spyware, by contrast, is designed to obtain covert or unauthorised access to information, device functions or communications. Advanced spyware can potentially access far more than a single motion sensor, including messages, files, location, microphone or camera data depending on the compromise.
For suspected device compromise, see Forensic Spyware and Malware Detection. NSI Global describes specialist forensic examination of mobile devices and endpoints for spyware, stalkerware, remote-access tools, persistence mechanisms and other indicators of compromise.
A Phone Can Be Monitored Without Conventional Spyware
Mobile surveillance can also occur at other layers. Stolen credentials may expose cloud accounts without installing anything on the handset. A telecommunications-level threat may target signalling or network infrastructure rather than the device operating system. A hidden microphone in a boardroom may collect conversations even when every phone in the room is clean.
That is why a useful investigation should not begin with the assumption that “spyware” is the answer. It should test competing explanations against the available evidence.
Related NSI analysis: Can a Mobile Phone Be Bugged Without Spyware? SS7 and Network-Based Surveillance.
Why This Matters to Executives, Boards and Sensitive Organisations
For an executive, lawyer, government official, investigator or senior employee, a mobile device routinely enters environments where commercially or legally sensitive information is discussed. The risk is therefore not limited to the contents of the phone. The device can sit beside board meetings, negotiations, privileged legal discussions, due-diligence work, strategic transactions and high-value travel.
A mature security posture looks across several layers at once: device compromise, application permissions, account security, cloud sessions, telecommunications exposure and the physical environment. The correct response depends on the threat model and the evidence – not on a generic checklist.
How to Reduce Mobile Sensor and Privacy Risk
For normal consumer and corporate use, the most effective controls are practical and proportionate. The goal is to reduce unnecessary access while preserving the ability to investigate unusual behaviour if a genuine concern arises.
- Keep the operating system, browser and applications current so that security and privacy fixes are applied promptly.
- Review app permissions periodically and remove access that is not necessary for the app’s legitimate function, particularly camera, microphone, location, Bluetooth, local-network and health-related access.
- Remove applications you no longer need and avoid sideloading software from untrusted sources. Official app stores reduce some risk but should not be treated as an absolute security guarantee.
- On iPhone and iPad, consider enabling App Privacy Report when you want greater visibility into recent sensor/data access and the domains contacted by apps.
- Use a strong device passcode and modern authentication for important accounts. For account passwords, current NIST guidance does not recommend arbitrary periodic changes; change credentials when compromise is suspected or confirmed, and use unique credentials or stronger authentication where supported.
- Treat unexpected permission requests as a reason to investigate the app’s purpose rather than simply accepting them.
- For corporate fleets, use mobile-device management and application governance to control software, permissions, updates and configuration at scale.
Closing Every Background App Is Not a Security Strategy
The original article advised users to close all background apps. That is not a reliable security control on modern smartphones. iOS and Android manage application lifecycle and background execution through platform rules, while malicious or compromised behaviour may involve services, accounts, permissions or exploits that are not meaningfully addressed by repeatedly swiping applications away.
The better approach is to manage permissions, keep software updated, remove untrusted applications and investigate credible indicators of compromise using evidence-based methods.
Do Not Factory-Reset a Phone Just Because You Suspect Surveillance
If the concern is ordinary privacy hygiene, changing settings or uninstalling an unnecessary app may be appropriate. If the phone may contain evidence of targeted surveillance, stalking, employee misconduct, cyber intrusion or another legal matter, a factory reset can destroy or alter valuable evidence.
Minimise unnecessary interaction with the suspected device and obtain device-specific forensic advice before resetting, restoring, updating, installing consumer “spyware detector” utilities or making extensive account changes. The preservation strategy should reflect the device state, legal context and the threat being investigated.
Related NSI capability: Digital Forensics.
When the Problem Is Bigger Than the Handset
A clean or inconclusive handset examination does not prove that communications are secure. The exposure may sit in an account, a telecommunications pathway or the physical environment. For higher-risk corporate and government users, the investigation may therefore need to combine digital forensics with communications security and Technical Surveillance Counter Measures.
NSI Global also provides Communications Security (COMSEC) for corporate and government sectors, including secure encrypted communications equipment and telecommunications-security capabilities.
Where the risk concerns the room, vehicle or meeting environment rather than the phone itself, see Technical Surveillance Counter Measures (TSCM).
How NSI Global Approaches a Suspected Mobile Surveillance Matter
The first task is to determine which surveillance hypothesis is technically plausible. Depending on the instruction and lawful authority, that can include reviewing the device state, installed applications, permissions, account and cloud evidence, communications artefacts, indicators of spyware or malware, linked devices, network-side concerns and the physical environment.
The result may be that no single “spy app” explains the concern. A defensible investigation should document what was examined, what was found, what could not be established, the limitations of the available evidence and which additional sources would materially improve the assessment.
Frequently Asked Questions
Can My Phone’s Accelerometer Reveal My PIN?
Research has shown that motion and orientation data can support PIN inference under controlled conditions. That does not mean an accelerometer can universally recover any user’s passcode. Success depends on the sensor data, sampling conditions, device interaction, model and platform restrictions.
Can Websites Access My Phone’s Motion Sensors?
It depends on the browser, API and platform. Modern web sensor access can be constrained by HTTPS requirements, permission mechanisms and Permissions-Policy controls. Some motion/orientation APIs also expose explicit permission requests in supported browsers. Behaviour is not identical across all browsers.
Can an App Use My Microphone or Camera Without Permission?
Under normal modern iOS and Android permission models, third-party applications must obtain the relevant permission to use protected camera and microphone functions. A compromised device or exploit may operate outside ordinary application assumptions, which is why permission settings alone cannot rule out advanced compromise.
Can a Phone Spy on Me Without Spyware?
Yes. Privacy exposure can arise from account compromise, cloud sessions, telecommunications-network threats, over-permissioned legitimate applications, sensor side channels or physical surveillance in the surrounding environment. Those mechanisms are technically different and require different investigative methods.
Should I Change My PIN and Passwords Regularly?
Do not rely on arbitrary periodic changes as the main security control. Use a strong device passcode, unique account credentials and stronger authentication where supported. Current NIST guidance states that account passwords should not be forced to change periodically without evidence of compromise; change them when compromise is suspected or confirmed.
Does Apple App Privacy Report Prove My iPhone Is Clean?
No. App Privacy Report can show recent access to certain privacy-sensitive data and device sensors, plus app and website network activity after the feature is enabled. It is useful for visibility, but it is not a substitute for forensic examination when advanced compromise is suspected.
Will Closing Background Apps Stop Sensor Spying?
Not reliably. Modern operating systems manage background activity themselves, and a surveillance concern may involve permissions, services, cloud accounts, browser activity or exploitation rather than a visibly open application. Review permissions and investigate the underlying cause instead.
Should I Factory-Reset a Phone if I Suspect Spyware?
Not if the matter may require evidence. A reset can remove or alter forensic artefacts. Minimise unnecessary changes and obtain specialist advice before resetting, restoring or installing diagnostic utilities on a potentially evidential device.
Can NSI Global Investigate Suspected Sensor or Mobile Surveillance?
NSI Global can assess suspected mobile-device compromise and related evidence under lawful authority. The appropriate scope depends on whether the concern points to an application or permission issue, spyware or malware, an account or cloud compromise, telecommunications exposure or a physical-surveillance threat.
Sources and Further Reading
- Newcastle University – Stealing PINs via Mobile Sensors: Actual Risk versus User Perception – The 2017 peer-reviewed research describing PINlogger.js and the reported PIN-inference results.
- Newcastle University – Are Your Sensors Spying on You? – Contemporary university summary of the original sensor-side-channel research and public-risk findings.
- Apple Platform Security – Protecting App Access to User Data – Apple documentation covering permission controls for camera, microphone, Bluetooth, Motion & Fitness and other protected data or hardware features.
- Apple Support – About App Privacy Report – Explains visibility into app access to privacy-sensitive data/sensors and network activity.
- Android Developers – Sensors Overview – Documents current Android sensor APIs and rate-limiting for certain motion and position sensors.
- Android Developers – Android 16 Behaviour Changes for Health and Fitness Permissions – Documents more granular health and body-sensor permission changes for apps targeting Android 16 or later.
- MDN – Sensor APIs – Explains permission and Permissions-Policy controls for modern web sensor APIs.
- MDN – DeviceMotionEvent.requestPermission() – Documents explicit permission requests for device-motion data in supporting browsers.
- NIST SP 800-63B-4 – Authentication and Authenticator Management – Current NIST guidance stating that passwords should not be changed periodically without evidence of compromise.
- NSI Global – Forensic Spyware and Malware Detection – NSI Global mobile and endpoint spyware/malware forensic capability.
- NSI Global – Communications Security (COMSEC) – NSI Global communications-security capability for corporate and government sectors.
- NSI Global – Technical Surveillance Counter Measures – NSI Global physical and electronic surveillance detection capability.